Blue Team Handbook: Incident Response (Paperback)
暫譯: 藍隊手冊:事件回應 (平裝本)
Murdoch, Don
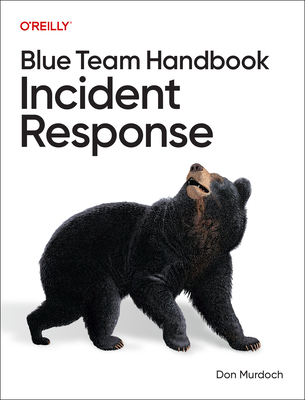
- 出版商: O'Reilly
- 出版日期: 2026-03-24
- 定價: $2,340
- 售價: 9.0 折 $2,106
- 語言: 英文
- 頁數: 356
- 裝訂: Quality Paper - also called trade paper
- ISBN: 9798341661264
- ISBN-13: 9798341661264
-
相關分類:
Penetration-test
立即出貨 (庫存 < 4)
Oreilly英文書展|任選2書8折 詳見活動內容 »
-
 90折
$2,592Data Engineering for Multimodal AI: Architecting Scalable Systems for Next-Generation AI Applications
-
90折
$2,592Data Engineering for Multimodal AI: Architecting Scalable Systems for Next-Generation AI Applications
-
 90折
$2,592Practical Mlflow for Generative AI on Databricks: Build High-Quality AI Agents from Prompt Design to Production
-
 90折
$2,457MLOps with Databricks: Machine Learning and Genai Applications End to End
-
 90折
$2,457An Illustrated Guide to AI Agents: Concepts and Code for Building Agents with Llms, Tools, and Memory
-
 90折
$2,520Blue Team Handbook: Soc, Siem, and Threat Hunting: Practical Techniques for Security Operations and Threat Hunting Teams
-
 90折
$1,944Building Agentic Solutions with Microsoft Foundry: Patterns, Workflows, and Best Practices for Intelligent Agents
-
 90折
$1,917Learning Cybersecurity Fundamentals: A Practical Guide to Essential Cybersecurity Concepts
-
 90折
$2,592Head First Algorithms and Data Structures: A Learner's Guide to the Foundations of Computing
-
 90折
$2,484Comptia Linux+ Study Guide: Essential Exam Prep
-
 90折
$2,520Video Generation with AI: Working with Diffusion Transformers and Multimodal Learning (Paperback)
-
 90折
$1,890Mapping Experiences: A Complete Guide to Activating Customer-Centered Collaboration 3/e
-
 90折
$2,493Databricks Certified Generative AI Engineer Associate Study Guide: Generative AI with Databricks
-
 90折
$2,502Ai-Assisted Statistics for Data Scientists: 50+ Essential Concepts Using R and Python
-
 90折
$2,268Observability Engineering: Achieving Production Excellence, 2/e (Paperback)
-
 90折
$1,935Soccer Analytics with Machine Learning: Learning Predictive Modeling Techniques with Sports Data
-
 90折
$1,926The C4 Model: Visualizing Software Architecture (Paperback)
-
 90折
$1,935Learning Cloud Security: Cloud Computing and Security Architecture Essentials
-
 90折
$2,502Vision Language Models: Building Vlms with Hugging Face (Paperback)
-
 90折
$2,142High Performance Spark: Best Practices for Scaling and Optimizing Apache Spark 2/e
-
 90折
$1,944Python for Excel: A Modern Environment for Automation and Data Analysis
-
 90折
$1,440Managing AI Projects: Drive Innovation and Successfully Navigate the Full AI Project Lifecycle (Paperback)
-
 90折
$2,520AI-Ready Data Blueprints: From Raw Data to Ai-Driven Innovation (Paperback)
-
 90折
$1,917Certified Kubernetes Application Developer (Ckad) Study Guide: In-Depth Guidance and Practice (Paperback)
-
 90折
$2,484Large Language Models: The Hard Parts: Open Source AI Solutions for Common Pitfalls (Paperback)
相關主題


商品描述
As cyberthreats grow and infrastructure evolves, organizations must prioritize effective, dynamic, and adaptable incident response. Based on the original print bestseller, Blue Team Handbook: Incident Response is now available for the first time in a digital format. This trusted and widely used field guide for cybersecurity incident responders, SOC analysts, and defensive security professionals distills incident response essentials into a concise, field-ready format.
Author Don Murdoch draws on decades of real-world experience in incident response and cybersecurity operations to provide actionable guidance and sample workflows you can immediately apply in your own work. Whether you're investigating an alert, analyzing suspicious traffic, or strengthening your organization's IR capability, you'll find this updated edition an essential resource for hands-on practitioners.
- Understand how modern adversaries operate and recognize common indicators of compromise in networks
- Analyze network traffic with common tools to identify and investigate suspicious activity
- Execute structured incident response procedures and follow a clear response plan
- Conduct basic forensic analysis on both Windows and Linux systems
- Use proven methodologies and tools to carry out effective, dynamic incident response
商品描述(中文翻譯)
隨著網路威脅的增長和基礎設施的演變,組織必須優先考慮有效、動態且可適應的事件響應。根據原版印刷暢銷書,藍隊手冊:事件響應 現在首次以數位格式推出。這本受信賴且廣泛使用的網路安全事件響應者、SOC 分析師和防禦安全專業人員的現場指南,將事件響應的基本要素提煉成簡明、現場準備好的格式。
作者 Don Murdoch 憑藉數十年的事件響應和網路安全操作的實際經驗,提供可行的指導和範例工作流程,您可以立即應用於自己的工作中。無論您是在調查警報、分析可疑流量,還是加強組織的事件響應能力,您都會發現這本更新版是實務工作者的重要資源。
- 了解現代對手的運作方式,並識別網路中的常見妥協指標
- 使用常見工具分析網路流量,以識別和調查可疑活動
- 執行結構化的事件響應程序並遵循明確的響應計劃
- 在 Windows 和 Linux 系統上進行基本的取證分析
- 使用經過驗證的方法和工具進行有效、動態的事件響應