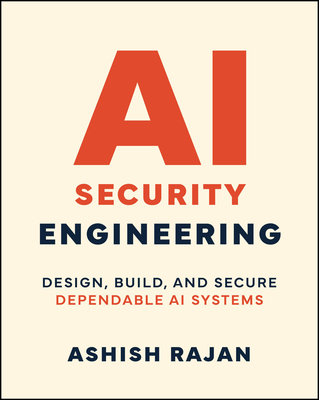
AI Security Engineering: Design, Build, and Secure Dependable AI Systems (Paperback)
暫譯: AI 安全工程:設計、建置與保護可靠的 AI 系統 (平裝本)
Rajan, Ashish
買這商品的人也買了...
-
 建構微服務|設計細微化的系統 (Building Microservices)
$580$458 -
 $474大數據之路:阿裡巴巴大數據實踐
-
 $351京東系統質量保障技術實戰
-
 管理技術債 (Managing Technical Debt)
$520$410 -
 軟體架構原理|工程方法 (Fundamentals of Software Architecture: A Comprehensive Guide to Patterns, Characteristics, and Best Practices)
$680$537 -
 單體式系統到微服務 (Monolith to Microservices)
$580$458 -
 $576架構演變實戰:從單體到微服務再到中臺
-
 Scaling Responsible AI: From Enthusiasm to Execution (Hardcover)
$1,450$1,377
相關主題

商品描述
Design, Build, and Secure Dependable AI Systems Across the Enterprise Lifecycle
AI is rapidly becoming part of core enterprise systems but most security programs were not designed for systems that are probabilistic, adaptive, and increasingly autonomous. AI Security Engineering provides a foundational, engineering-first playbook for designing, operating, and scaling secure AI systems across the enterprise lifecycle.
Written by Ashish Rajan, a CISO advising Fortune 500 organizations on AI security, this book focuses on security for AI systems not AI used as a security tool. It examines how AI changes traditional security assumptions and how organizations must adapt their architectures, pipelines, governance models, and operating practices to manage AI risk effectively in production environments.
Rather than focusing on tools or point solutions, AI Security Engineering applies security engineering principles to modern AI systems. It covers AI threat models, secure AI pipelines, runtime detection and incident response, governance and compliance at scale, and the emerging challenges of agentic and multi-model systems. Readers are guided through how to evolve existing security programs to support AI-enabled applications without slowing delivery or becoming the "department of no".
This book shows how to:
- Design and operate secure AI systems across their full lifecycle from architecture and delivery to operations and scale
- Defend production AI applications against adversarial, emergent, and agent-driven threats
- Embed governance and risk controls into AI pipelines using engineering-first approaches
- Operate AI security in dynamic environments, including third-party and agentic systems
- Balance regulatory compliance, system performance, and engineering velocity
CISOs seeking strategic clarity for AI security investments, security architects designing resilient systems, and engineers responsible for operating AI in production will find this book a durable reference for building dependable AI systems at enterprise scale.
設計、建置並保護貫穿企業生命週期的可靠 AI 系統
AI 正迅速成為企業核心系統的一部分,但多數安全計畫並非為具備機率性、適應性且日益自主化的系統而設計。《AI Security Engineering》提供一套以工程為優先的基礎實務指南,協助企業在整個生命週期中設計、運作及擴展安全的 AI 系統。
本書由 Ashish Rajan 撰寫;他是為《Fortune》500 大企業提供 AI 安全諮詢的 CISO。本書聚焦於 AI 系統本身的安全,而非將 AI 用作安全工具。書中探討 AI 如何改變傳統的安全假設,以及組織必須如何調整其架構、管線、治理模型與營運實務,才能在正式生產環境中有效管理 AI 風險。
《AI Security Engineering》不著重於工具或單點解決方案,而是將安全工程原則應用於現代 AI 系統。內容涵蓋 AI 威脅模型、安全 AI 管線、執行期偵測與事件回應、大規模治理與合規,以及代理式(agentic)和多模型系統所帶來的新興挑戰。本書將引導讀者了解如何演進現有的安全計畫,以支援啟用 AI 的應用程式,同時不拖慢交付速度,也不成為阻礙創新的「拒絕部門」。
本書將說明如何:
• 在 AI 系統的完整生命週期中進行設計與營運,涵蓋架構、交付、操作及擴展
• 防禦正式環境中的 AI 應用程式,抵抗對抗式、新興及由代理驅動的威脅
• 採用以工程為優先的方法,將治理與風險控制嵌入 AI 管線
• 在動態環境中執行 AI 安全,包括第三方系統與代理式系統
• 在法規合規、系統效能與工程開發速度之間取得平衡
對於尋求 AI 安全投資策略方向的 CISO、負責設計韌性系統的安全架構師,以及負責在正式環境中運作 AI 的工程師而言,本書將是建立企業規模可靠 AI 系統時值得長期參考的指南。
以上中文內容由 AI 翻譯