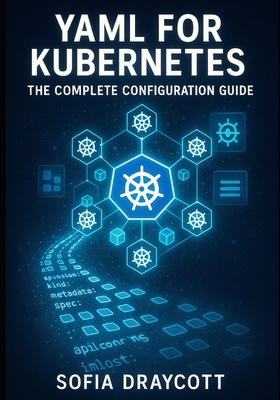
Yaml for Kubernetes: THE COMPLETE CONFIGURATION GUIDE: Master Manifests, Helm Charts, and Kustomize. From Pods to Production Deployments with Best Pra
暫譯: Kubernetes 的 YAML:完整設定指南:掌握 Manifest、Helm Charts 與 Kustomize,從 Pod 到正式環境部署的最佳實務
Draycott, Sofia
- 出版商: Independently Published
- 出版日期: 2025-11-15
- 售價: $1,330
- 貴賓價: 9.5 折 $1,263
- 語言: 英文
- 頁數: 306
- 裝訂: Quality Paper - also called trade paper
- ISBN: 9798274621137
- ISBN-13: 9798274621137
-
相關分類:
Kubernetes、DevOps、CI/CD
海外代購書籍(需單獨結帳)
相關主題


商品描述
Master Kubernetes configuration with clear YAML, proven patterns, and production ready workflows.
Struggling to keep Kubernetes manifests, Helm charts, and Kustomize overlays consistent across dev, staging, and production clusters can drain time and confidence. Small changes in YAML often have big effects on Pods, Services, security, and traffic, and it is not always obvious why something broke.
YAML FOR KUBERNETES: THE COMPLETE CONFIGURATION GUIDE walks you through real Kubernetes configuration from first manifest to full GitOps driven, multi tenant environments. You will see how to express intent clearly in YAML, validate and secure it, and operate it safely in real clusters.
- Understand how Kubernetes reads and applies YAML, including apiVersion, kind, metadata, spec, and status.
- Write reliable Pod specs, Deployments, ReplicaSets, StatefulSets, DaemonSets, Jobs, and CronJobs for real applications.
- Configure Services, Ingress, headless Services, DNS, and NetworkPolicies for clear traffic flow and practical isolation.
- Manage ConfigMaps, Secrets, volumes, PersistentVolumeClaims, and StorageClasses for twelve factor style applications.
- Set resource requests and limits, probes, affinity, tolerations, topology spread constraints, PodDisruptionBudgets, and rollout strategies that behave well under load.
- Apply validation and policy with kubeconform, kubeval, linters, Pod Security Standards, securityContext fields, Kyverno, and Gatekeeper.
- Build and operate Helm charts, from Chart.yaml and values.yaml through templating, testing, versioning, upgrades, and rollbacks.
- Use Kustomize bases, overlays, patches, transformers, and generators to keep configuration template free but flexible.
- Work with CustomResourceDefinitions and custom resources safely, including schemas, versioning, conversion, and common CRDs like Gateway API and Argo CD.
- Design Git repositories, GitOps flows with Argo CD Applications and ApplicationSets, Flux Kustomizations and HelmReleases, and multi tenant setups with namespaces, RBAC, and policy boundaries.
- Troubleshoot failed deployments, misconfigurations, and anti patterns using practical production checklists and refactoring examples.
This is a code heavy guide with complete YAML manifests, kubectl commands, Helm values, Kustomize kustomization.yaml files, and real CRD examples so you can adapt working configuration directly into your own clusters.
Grab your copy today and make your Kubernetes configuration predictable, secure, and production ready.
商品描述(中文翻譯)
掌握 Kubernetes 設定,透過清晰的 YAML、經驗驗證的模式,以及適用於正式環境的工作流程,打造可靠的 Kubernetes 環境。
如果要讓 Kubernetes manifests、Helm charts 和 Kustomize overlays 在開發、預備與正式環境叢集之間保持一致,往往會耗費大量時間,也容易削弱信心。YAML 中的微小變更,經常會對 Pods、Services、安全性與流量造成重大影響,而且問題發生的原因不一定顯而易見。
《YAML FOR KUBERNETES: THE COMPLETE CONFIGURATION GUIDE》將帶你逐步了解真實世界中的 Kubernetes 設定,從第一個 manifest,一直到完整的 GitOps 驅動多租戶環境。你將學會如何在 YAML 中清楚表達意圖、進行驗證與保護,並在實際叢集中安全地操作。
• 了解 Kubernetes 如何讀取並套用 YAML,包括 apiVersion、kind、metadata、spec 和 status。
• 為實際應用程式撰寫可靠的 Pod specs、Deployments、ReplicaSets、StatefulSets、DaemonSets、Jobs 和 CronJobs。
• 設定 Services、Ingress、headless Services、DNS 和 NetworkPolicies,實現清晰的流量流程與實用的隔離機制。
• 管理 ConfigMaps、Secrets、volumes、PersistentVolumeClaims 和 StorageClasses,以支援 Twelve-Factor 風格的應用程式。
• 設定 resource requests 和 limits、probes、affinity、tolerations、topology spread constraints、PodDisruptionBudgets,以及在負載下仍能正常運作的 rollout strategies。
• 使用 kubeconform、kubeval、linters、Pod Security Standards、securityContext 欄位、Kyverno 和 Gatekeeper 實施驗證與政策控管。
• 建置與操作 Helm charts,涵蓋從 Chart.yaml 和 values.yaml,到模板化、測試、版本管理、升級與 rollback 的完整流程。
• 使用 Kustomize bases、overlays、patches、transformers 和 generators,讓設定不必依賴模板,同時保有彈性。
• 安全地使用 CustomResourceDefinitions 和 custom resources,包括 schemas、versioning、conversion,以及 Gateway API 和 Argo CD 等常見 CRDs。
• 設計 Git repositories、使用 Argo CD Applications 與 ApplicationSets、Flux Kustomizations 與 HelmReleases 建立 GitOps 流程,並透過 namespaces、RBAC 和 policy boundaries 建構多租戶環境。
• 使用實用的正式環境檢查清單與重構範例,針對失敗的 deployments、錯誤設定與反模式進行疑難排解。
這是一本高度重視程式碼實作的指南,提供完整的 YAML manifests、kubectl 指令、Helm values、Kustomize kustomization.yaml 檔案,以及真實的 CRD 範例,讓你能直接將可運作的設定調整後套用到自己的叢集中。
立即入手,讓你的 Kubernetes 設定變得可預測、安全,並符合正式環境的需求。